PFALZKOM’s Hybrid DDoS Layered Protection Model
A Shield for Your IT: How PFALZKOM’s Hybrid Layered Defense Model Stops DDoS Attacks in Their Tracks, and Why a Simple Firewall Is No Longer Enough in Cyberspace
Anyone who wants to protect their corporate IT from attackers today can no longer think in terms of simple walls. Modern cyberattacks are highly dynamic, adaptable, and often multi-pronged. While one attack vector attempts to flood Internet bandwidth, another simultaneously aims to cripple application servers through targeted, seemingly legitimate queries.
After highlighting the strategic importance of overload protection in our last article, today we’ll take a closer look at the technical architecture of the new PFALZKOM DDoS protection. The secret lies in a hybrid, multi-layered model that we’ve implemented in close collaboration with the German market leader, Myra Security. A key highlight here is that a significant portion of this line of defense is operated directly in PFALZKOM’s own data centers, which are equipped with state-of-the-art software and hardware.
The Principle of Street Cleaning: What Is a Scrubbing Center?
To understand how the layered model works, it helps to think of it as a modern water filtration system. Instead of allowing unfiltered raw water to flow directly into end-users’ pipes, it is first purified through various filtration stages.
In the context of DDoS protection, IT experts refer to this process as “traffic scrubbing”. All incoming data traffic destined for your IP addresses or domains is continuously rerouted through our protection layers – or immediately in the event of an emergency. There, high-performance filtering algorithms analyze every single data packet in milliseconds. Malicious data is immediately isolated and discarded, while legitimate traffic is forwarded to your servers without any noticeable delay.
The Protection Layers in Detail: Local Precision Meets Global Cloud Power
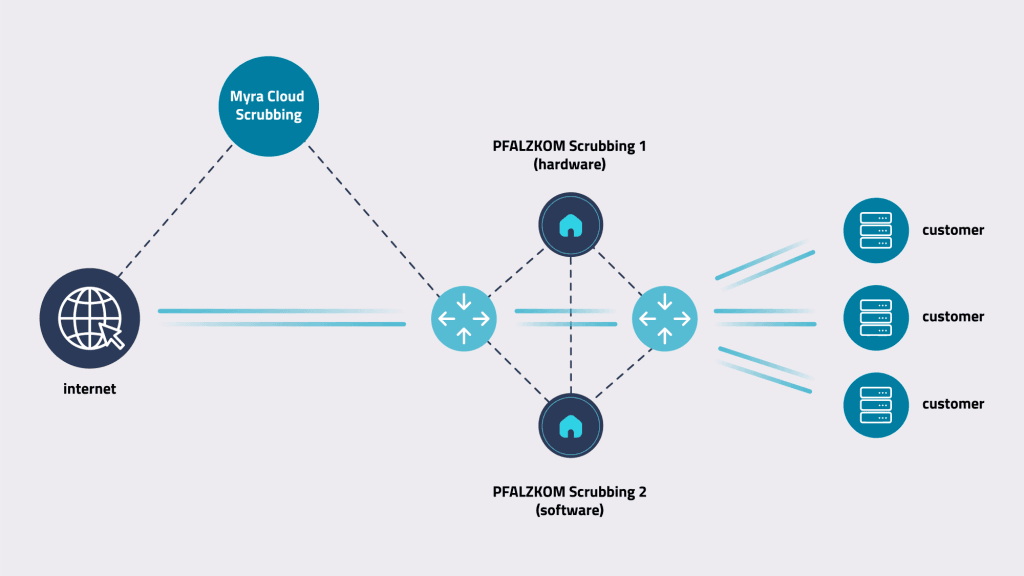
As shown in the architecture diagram above, our security strategy is divided into two fundamental, intelligently interconnected pillars that neutralize different types of attacks across the various OSI layers. We distinguish between basic infrastructure protection (Layers 3 and 4) and specialized projects at the application layer (Layer 7).
Protection Layer 1: Local on-premises scrubbing at the PFALZKOM Data Center
Several dedicated, high-performance security appliances are integrated directly into PFALZKOM’s Data Centers; these are optimally tailored to our network infrastructure in terms of both software and hardware. This local layer of protection uses advanced monitoring to track traffic flows in real time. As soon as predefined thresholds are exceeded, filtering is activated fully automatically.
- What is being filtered here? This layer is highly granular. It defends against protocol-based and volumetric attacks at the network layer.
- The PFALZKOM Advantage: Because this appliance runs directly in our Data Center, we can protect even small IP subnets. Customer data remains within our physical, regional infrastructure or is transmitted over our network – an invaluable advantage for ensuring compliance with strict data protection and compliance guidelines (GDPR).
Protection Layer 2: Global Myra Cloud Scrubbing for Extremely High Volumes
In so-called volumetric attacks (e.g., UDP reflection or flood attacks), such enormous amounts of data are generated that they would simply overwhelm the physical capacity of a Data Center’s Internet uplinks.
At that moment, the second, upstream layer of protection in the cloud kicks in. Through Myra Security’s infrastructure, traffic is seamlessly routed via a global network of high-capacity scrubbing centers during extreme traffic surges. This cloud infrastructure has massive bandwidth capacity and effortlessly defends against even extreme attacks (at several terabits per second) before they even reach our regional network.
Regardless of the traditional network connection, highly complex security concepts can be implemented for HTTP/HTTPS applications. Since this requires a customized technical approach, we plan such projects directly with you and our partner Myra – tailored precisely to your application landscape.
The Core Technical Features and Their Associated Benefits
The combination of local hardware precision and global cloud power enables a range of capabilities that goes far beyond simply defending against attacks:
- Advanced GeoIP Blocking & Rate Limiting: You can specifically control which countries or regions are allowed to access your systems. If you do not expect customers from certain overseas regions, the system proactively blocks suspicious IP ranges from those areas. In addition, rate limiting regulates how many requests a single IP address is allowed to make within a given time period, which reliably slows down bots.
- Real-Time Upstream Monitoring: The system monitors your network connection around the clock. In the event of irregularities or acute threats, our systems automatically coordinate with one another to prevent outages and ensure normal operations.
- Optional – Full transparency through detailed reporting: After every attack is mitigated, B2B customers receive a detailed, customized report. They can see exactly when the attack took place, which methods (e.g., SYN flood or HTTP targeting) were used, and how intense the attack peak was. This provides valuable evidence for audits, insurance purposes, or management.
Conclusion: Your Digital Life Insurance from the Region
PFALZKOM DDoS Protection combines the best of both worlds: the uncompromising, global defense capabilities of a KRITIS-certified cloud platform with the maximum data sovereignty and flexibility of a premium regional Data Center right on your doorstep.
With our sophisticated layers of protection and the ability to provide highly effective protection even for individual IP addresses, we offer a customized security solution for discerning B2B small and medium-sized businesses. Make your digital infrastructure more resilient against denial-of-service attacks and ensure the uptime of your business processes.
Interested in learning more? Our experts would be happy to work with you to analyze your existing infrastructure and develop a comprehensive and reliable security plan. Please contact us!